CISA contractor apparently leaked 'highly sensitive' government AWS keys on Github
4 distinct publishers, one article each in this sample.
Ownership mix: Other: 4
4 publishers · 4 articles · switch to 1-minute for disagreement and framing.
What happened
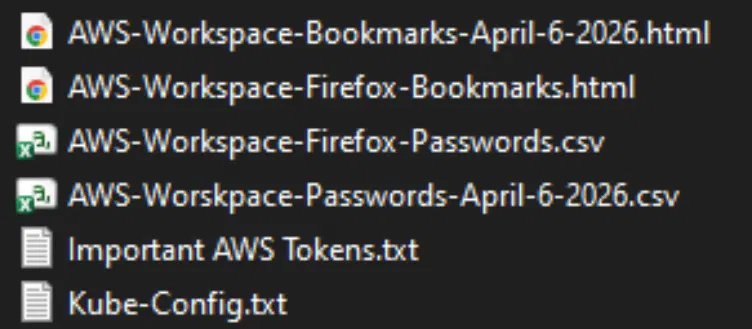
Until this past weekend, a contractor for the Cybersecurity & Infrastructure Security Agency (CISA) maintained a public GitHub repository that exposed credentials to several highly privileged AWS GovCloud accounts and…
Why the coverage differs
AI-assisted comparison · labeled · generated May 23, 2026, 7:46 AM · not a verdict
A contractor for the Cybersecurity & Infrastructure Security Agency (CISA) reportedly exposed sensitive credentials for AWS GovCloud accounts on a public GitHub repository. The incident raises concerns about cybersecurity protocols and the handling of sensitive information by government contractors.
Coverage among the outlets remains largely similar, with all emphasizing the leak's potential implications for national security. However, TechRadar's framing includes stronger language, describing the leak as "one of the most egregious government data leaks in recent history," which adds a more alarmist tone compared to the more neutral reports from Krebsonsecurity, r/cybersecurity, and r/technology. The latter three focus primarily on the facts of the incident without sensationalizing the consequences.
Comparison summary
AI-assisted · Cerebras / Llama · May 23, 2026, 7:46 AM · inspect sources below rather than trusting this alone
A contractor for the Cybersecurity & Infrastructure Security Agency (CISA) reportedly exposed sensitive credentials for AWS GovCloud accounts on a public GitHub repository. The incident raises concerns about cybersecurity protocols and the handling of sensitive information by government contractors.
Coverage among the outlets remains largely similar, with all emphasizing the leak's potential implications for national security. However, TechRadar's framing includes stronger language, describing the leak as "one of the most egregious government data leaks in recent history," which adds a more alarmist tone compared to the more neutral reports from Krebsonsecurity, r/cybersecurity, and r/technology. The latter three focus primarily on the facts of the incident without sensationalizing the consequences.
No outlet has provided detailed information on the specific security measures that were in place prior to the leak or any potential repercussions for the contractor involved. This lack of context may leave readers without a full understanding of the incident's significance and the broader implications for cybersecurity practices within government agencies.
Report timeline
Oldest → newest among clustered members. Gaps may mean delayed pickup, not silence.
-
May 18, 2026, 3:20 PMKrebsonsecurity · CenterCISA Admin Leaked AWS GovCloud Keys on Github
-
May 18, 2026, 5:47 PMReddit · CenterCISA Contractor Admin Leaked AWS GovCloud Keys on Github
-
May 18, 2026, 7:41 PMReddit · CenterCISA Admin Leaked AWS GovCloud Keys on Github
-
May 19, 2026, 8:20 AM
Coverage by perspective
Perspective labels are external consensus ratings (AllSides / Ad Fontes / MBFC-style), not WeSearch truth scores. Center is not automatically more accurate.
Center · 4
Headline framing
Vocabulary fingerprints · not a political endorsement
The headlines report on a leak of AWS GovCloud keys by a CISA admin or contractor, with one emphasizing the sensitivity of the information.
Bias/ownership: published methodology on source profiles · AI text always labeled · no reader paywall · no engagement ranking of news · transparency · contribute Ws · home