BragJack attacks hijack AI browser agents through malicious extensions
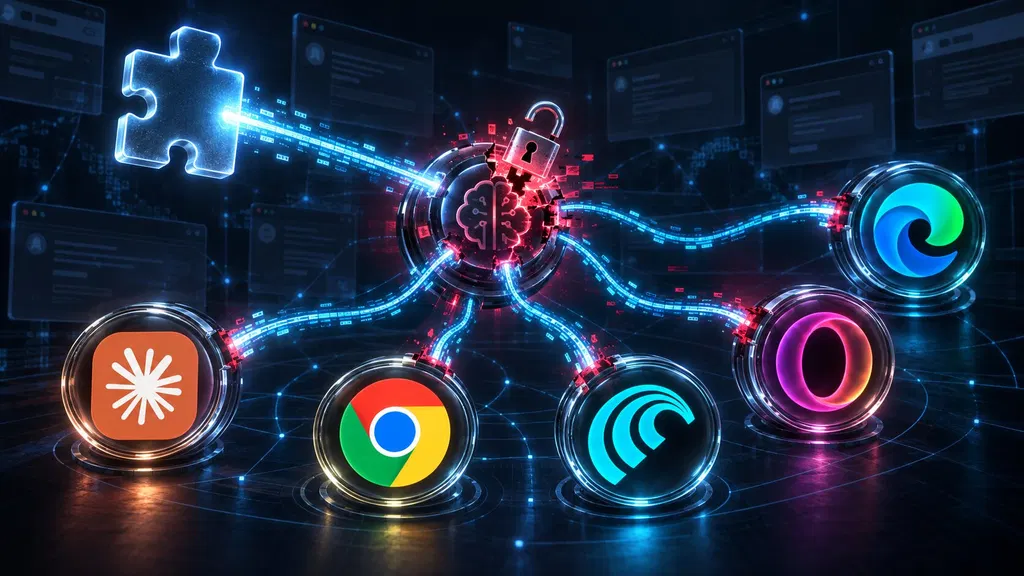
Security researcher Gal Weizman disclosed a new attack technique called BragJack that hijacks AI browser agents through malicious extensions. The proof-of-concept successfully compromised five Chromium-based browsers and assistants by exploiting trusted browser components and network request manipulation. Vendors resolved the identified flaws, resulting in two CVEs and over $20,000 in bug bounties.
- ▪The BragJack attack uses the Chromium declarativeNetRequest functionality to manipulate web traffic and inject code into privileged AI components.
- ▪The technique was demonstrated against Google Chrome's Gemini Live, Perplexity Comet, Microsoft Edge, Opera Neon, and Anthropic's Claude in Chrome.
- ▪Researchers earned more than $20,000 in bug bounties from the five affected vendors for disclosing the vulnerabilities.
- ▪Both Google and Microsoft have resolved the specific flaws assigned to them, which included CVE-2026-0628 and CVE-2026-55945.
- ▪The attack allows malicious extensions to access sensitive data such as local files, screenshots, and browsing history without user interaction.
Hacker News (AI / LLM) files mainly under ai. We currently carry 5,712 of its stories.
Story provenance
Source · retrieval · rights · ranking — open for full record
inspect →
Story provenance
Attribution is not the same as permission. This drawer separates discovery metadata, excerpts, WeSearch-generated summaries, reuse status, and whether the publisher receives the visit. Nothing here claims a legal grant the publisher has not made.
Record
| Original publisher | BleepingComputer |
| Canonical URL | https://www.bleepingcomputer.com/news/security/bragjack-attacks-hijack-ai-browser-agents-through-malicious-extensions/ |
| Publication time | Sun, 20 Sep 2026 13:07:09 +0000 |
| Retrieval time | 2026-09-20T13:23:48.424Z |
| Last seen | 2026-09-20T13:23:48.424Z |
| Headline source | Publisher (no WeSearch rewrite) |
| Excerpt source | publisher body |
| Excerpt method | First ~120 words (~800 chars) of extracted publisher body, fair-use limited. |
| Summary | WeSearch · cerebras-chat (WeSearch summarizer) |
| Summary source text | contentText |
| Citation coverage | Summary is a WeSearch-generated derivative; primary citation is the original publisher URL. |
| Cluster | Osk4OiLZ8a7z · 1 stories |
| Cluster logic | Grouped by semantic title/content similarity across sources within a rolling window. Same-publisher template collisions are excluded from coverage comparison. |
| Ranking reason | Story pages are not engagement-ranked. Hub feeds use recency, with optional source-diversified chronological ordering (cap consecutive stories per source). No personalized ranking. |
| Publisher visit | Yes — open original |
| Substitutes article? | No — link-out required for full text |
Rights status (four layers)
WeSearch handling by dimension
| Indexing | May the item be indexed (stored, ranked, made findable)? | Allowed |
| Snippet | May a short excerpt of the publisher's text be shown? | Allowed |
| AI summary | May WeSearch generate its own short summary of the article? | Limited |
| Retrieval / RAG | May the content be exposed for third-party retrieval-augmented generation? | Not asserted |
| Model training | May the content be used to train AI models? | Not asserted |
| Commercial reuse | May the content be reused commercially? | Not permitted |
Basis: Derived from the published RSS/Atom feed. Contact: [email protected]. Reviewed: 2026-07-24.
Opening excerpt (first ~120 words) tap to expand
BragJack attacks hijack AI browser agents through malicious extensions By Ax Sharma September 19, 2026 10:56 AM 0 Security researcher Gal Weizman of Forever Security has disclosed a new attack technique that can hijack the AI assistants built into popular browsers using a single malicious browser extension. Dubbed BragJack, the proof-of-concept was demonstrated against five Chromium-based browsers or browser assistants: Google Chrome's Gemini Live, Perplexity Comet, Microsoft Edge, Opera Neon, and Anthropic's Claude in Chrome. The research earned more than $20,000 in bug bounties from the five vendors, ranging from $600 to $7,000, and produced two CVEs. The attack requires the malicious extension to already be installed in the victim's browser.
…
Excerpt limited to ~120 words for fair-use compliance. The full article is at BleepingComputer.
Discussion
0 commentsMore from BleepingComputer