Malicious VPN config files can let attackers run commands on Asus routers
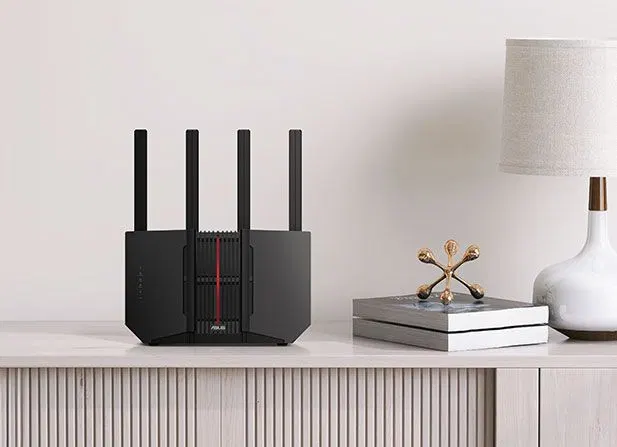
When you purchase through links on our site, we may earn an affiliate commission. Asus names firmware series rather than models: 3.0.0.6_102 for both bugs, with the 3.0.0.4_386 and 3.0.0.4_388 series also affected by the Telnet one.The routers can act as a VPN client when set up with a configuration file from a VPN provider. Things go wrong when crafted text inside the uploaded files is read as formatting instructions rather than plain data.
- ▪When you purchase through links on our site, we may earn an affiliate commission.
- ▪Asus names firmware series rather than models: 3.0.0.6_102 for both bugs, with the 3.0.0.4_386 and 3.0.0.4_388 series also affected by the Telnet one.The routers can act as a VPN client when set up with a configuration file from a VPN provi
- ▪Things go wrong when crafted text inside the uploaded files is read as formatting instructions rather than plain data.
Tom's Hardware files mainly under tech. We currently carry 909 of its stories.
Story provenance
Source · retrieval · rights · ranking — open for full record
inspect →
Story provenance
Attribution is not the same as permission. This drawer separates discovery metadata, excerpts, WeSearch-generated summaries, reuse status, and whether the publisher receives the visit. Nothing here claims a legal grant the publisher has not made.
Record
| Original publisher | Tom's Hardware |
| Canonical URL | https://www.tomshardware.com/tech-industry/cyber-security/malicious-vpn-config-files-can-let-attackers-run-commands-on-asus-routers-companys-patch-also-fixes-a-bug-that-lets-a-logged-in-attacker-switch-on-telnet-with-root-access |
| Publication time | Sat, 03 Oct 2026 12:30:00 +0000 |
| Retrieval time | 2026-10-03T12:38:12.806Z |
| Last seen | 2026-10-03T12:38:12.806Z |
| Headline source | Publisher (no WeSearch rewrite) |
| Excerpt source | publisher body |
| Excerpt method | First ~120 words (~800 chars) of extracted publisher body, fair-use limited. |
| Summary | WeSearch · cerebras-chat (WeSearch summarizer) |
| Summary source text | contentText |
| Citation coverage | Summary is a WeSearch-generated derivative; primary citation is the original publisher URL. |
| Cluster | QC4vKYaLjuMz · 1 stories |
| Cluster logic | Grouped by semantic title/content similarity across sources within a rolling window. Same-publisher template collisions are excluded from coverage comparison. |
| Ranking reason | Story pages are not engagement-ranked. Hub feeds use recency, with optional source-diversified chronological ordering (cap consecutive stories per source). No personalized ranking. |
| Publisher visit | Yes — open original |
| Substitutes article? | No — link-out required for full text |
Rights status (four layers)
WeSearch handling by dimension
| Indexing | May the item be indexed (stored, ranked, made findable)? | Allowed |
| Snippet | May a short excerpt of the publisher's text be shown? | Allowed |
| AI summary | May WeSearch generate its own short summary of the article? | Limited |
| Retrieval / RAG | May the content be exposed for third-party retrieval-augmented generation? | Not asserted |
| Model training | May the content be used to train AI models? | Not asserted |
| Commercial reuse | May the content be reused commercially? | Not permitted |
Basis: Derived from the published RSS/Atom feed. Contact: [email protected]. Reviewed: 2026-07-24.
Opening excerpt (first ~120 words) tap to expand
Tech Industry Cybersecurity Malicious VPN config files can let attackers run commands on Asus routers — company’s patch also fixes a bug that lets a logged-in attacker switch on Telnet with root access News By Shane Downing Published 3 October 2026 Asus rates the VPN-file flaw as critical, scoring at 9.4 out of 10 on CVSS 4.0. When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works. (Image credit: Asus) Copy link Facebook X Whatsapp Reddit Pinterest Flipboard Email Share this article 0 Join the conversation Follow us Add us as a preferred source on Google Newsletter Subscribe to our newsletter A “crafted VPN client configuration file” uploaded by the user or a logged-in attacker via an Asus router’s web management interface can allow an…
Excerpt limited to ~120 words for fair-use compliance. The full article is at Tom's Hardware.
Discussion
0 commentsMore from Tom's Hardware